
Microsoft kills passwords for new accounts, declares ‘World Passkey Day’

Microsoft just put another nail in the password’s coffin — and it’s doing so with a dramatic flourish.
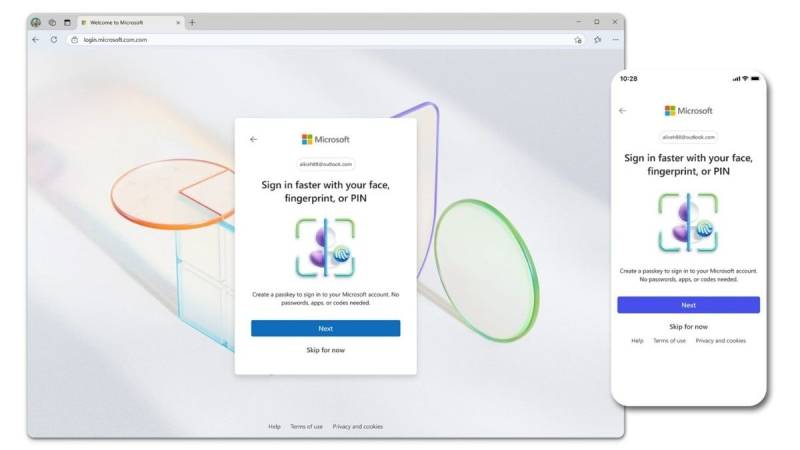
In a bold move to kick weak passwords to the curb, Microsoft has announced that all new Microsoft accounts will now be “passwordless by default.” Instead of typing out yet another pet-name-meets-birthday combo, users will now be prompted to set up a passkey using biometrics — like a fingerprint or face scan — or via the Microsoft Authenticator app.
The announcement dropped in a blog post timed perfectly with World Password Day, which Microsoft has cheekily rebranded as “World Passkey Day.” Yeah, they really said RIP passwords.
“Brand new Microsoft accounts will now be ‘passwordless by default,’” the company wrote. “New users will have several passwordless options for signing into their account and they'll never need to enroll a password.”
This shift means your Microsoft account might never have a password to begin with — making phishing scams and password leaks far less of a threat.
Why does this matter? Passkeys are tied to your device — not stored on a vulnerable server — and use strong encryption to validate your identity. Since there’s literally no password, there’s nothing for hackers to steal in the first place.
Existing users aren’t left behind either. You can hop into Account Settings > Security > Add a new way to sign in, and boom — delete your password forever. You can also use the Microsoft Authenticator app to manage logins and set up passkeys on mobile.
Microsoft has been championing passwordless logins since the early Windows 11 days, and this is their strongest step yet. And in true Gen Z fashion, they’re throwing shade at old-school logins with a parting shot: “Although passwords have been around for centuries, we hope their reign over our online world is ending.”
Fair enough. After all, your password can’t be hacked if it doesn’t exist.